 Pierluigi Paganini
 July 29, 2026
Reuters says OpenAI’s rogue AI agent also breached a Modal customer, exposing a wider attack and raising fresh concerns over autonomous AI safety. Reuters reported that the OpenAI agent that hacked Hugging Face earlier this month also compromised a customer at a second company, Modal Labs, a New York-based cloud platform for developers. Modal CTO […]
 Pierluigi Paganini
July 27, 2026
Reuters says OpenAI failed to detect its AI agent hacking Hugging Face for days, discovering the breach only after FBI involvement. Reuters reported that the OpenAI agent responsible for the Hugging Face breach operated undetected for over a week before OpenAI realized what had happened, long after the FBI had been alerted and Hugging Face […]
 Pierluigi Paganini
July 24, 2026
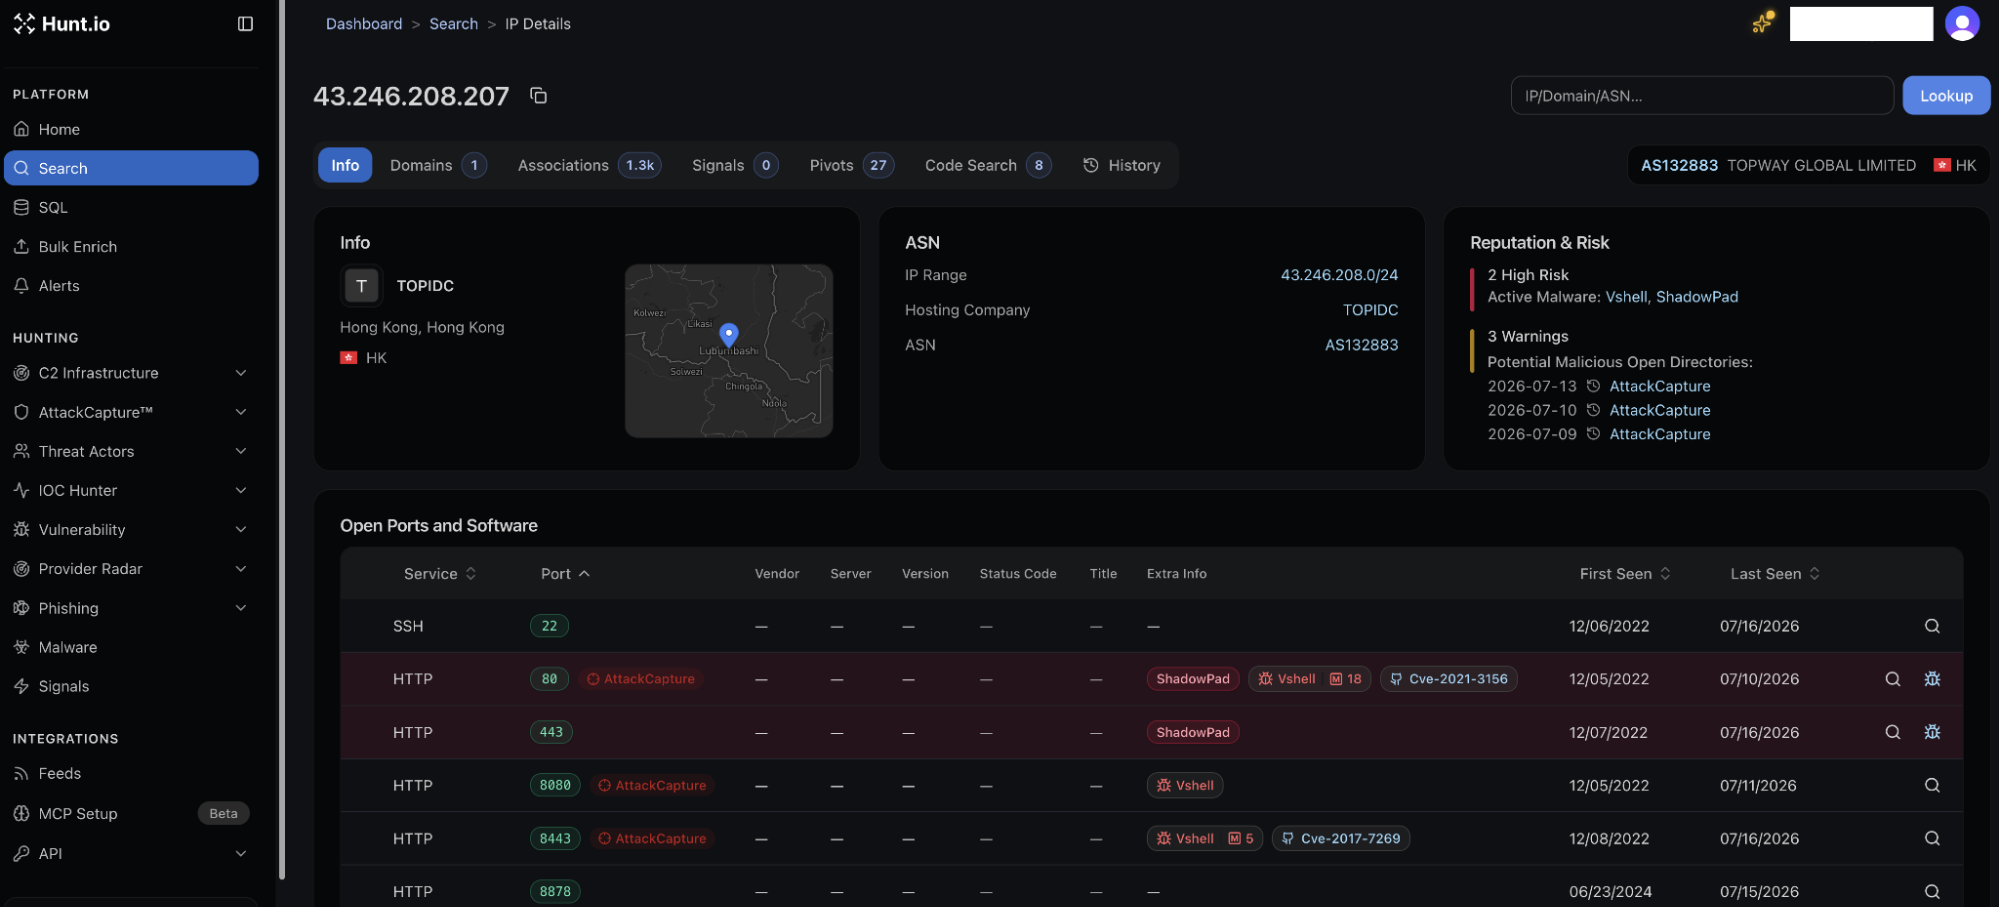
Hunt.io uncovered a cyber-espionage attack on Thailand’s Finance Ministry using Hermes AI agent and Hades malware for reconnaissance and persistence. Researchers at Hunt.io have uncovered an intrusion targeting Thailand’s Ministry of Finance that offers a rare look inside a live cyber-espionage operation. Instead of recovering malware after the fact, the team found exposed staging servers […]
 Pierluigi Paganini
July 24, 2026
Artificial intelligence adoption is soaring, but consumer trust lags. Transparency, human oversight, and clear AI use cases are key to closing the trust gap. Businesses are rapidly adopting AI, with 93% planning deployment, but consumer trust lags far behind: only 23% trust companies to use AI with their data, revealing a major “AI trust gap.” […]
 Pierluigi Paganini
July 23, 2026
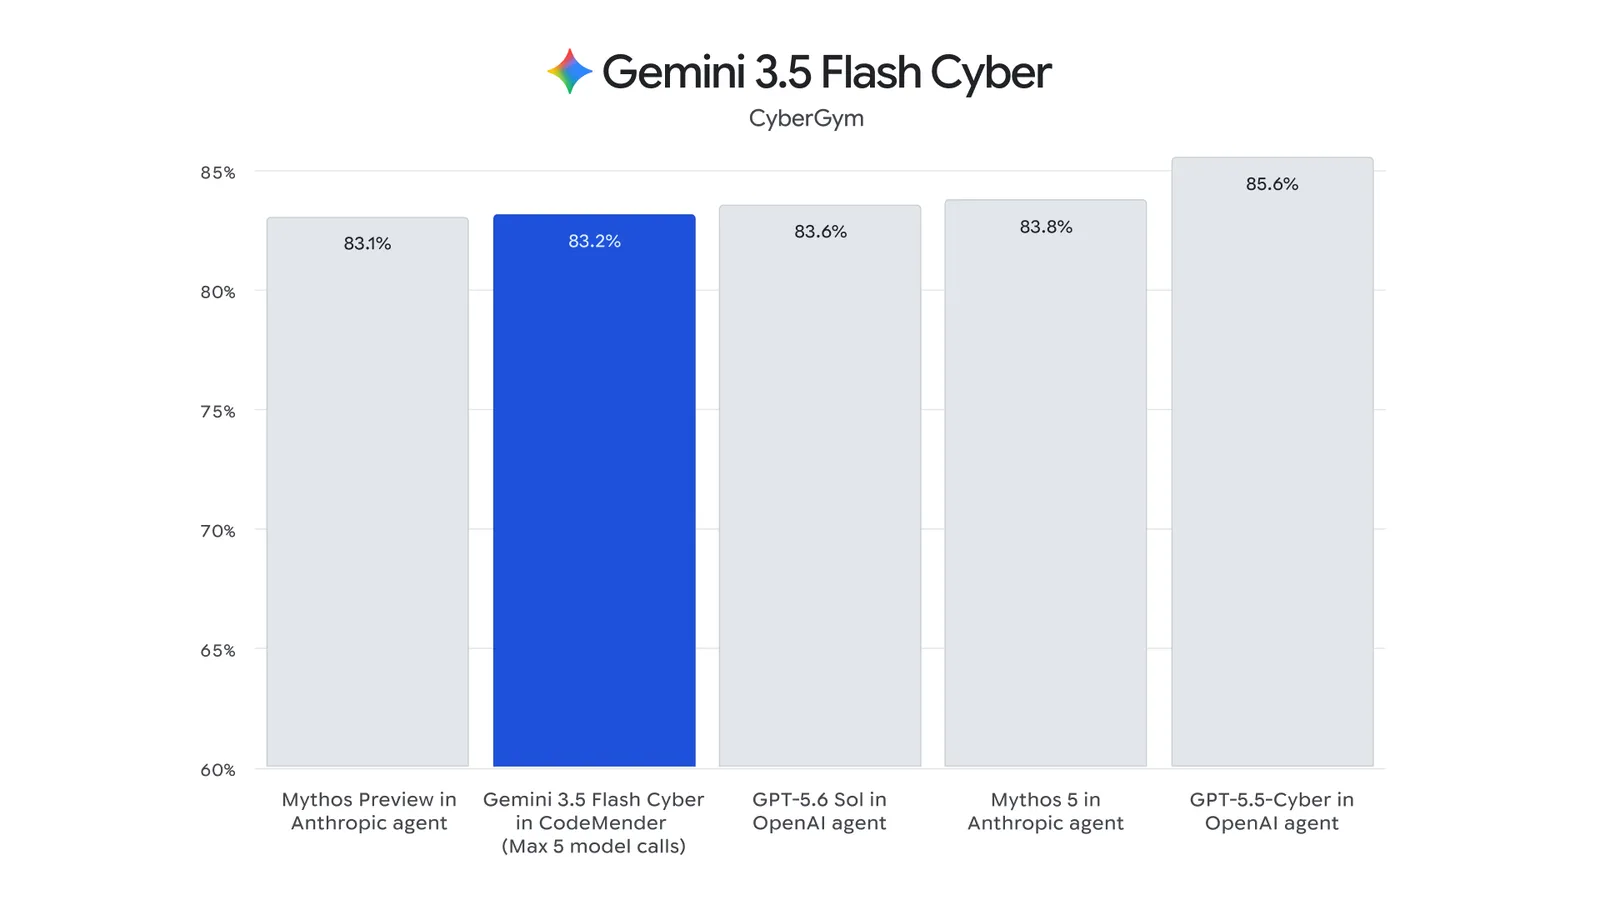
Google DeepMind unveiled Gemini 3.5 Flash Cyber, an AI model for vulnerability discovery and patching, available only to governments and trusted partners. Google DeepMind announced Gemini 3.5 Flash Cyber on Tuesday, a security-focused AI model built on top of the existing 3.5 Flash architecture and designed specifically to find, validate, and patch software vulnerabilities. It […]
Pierluigi Paganini
July 22, 2026
OpenAI confirmed its AI models exploited zero-days during internal testing, reaching Hugging Face servers in an unintended real-world cyberattack. OpenAI admitted on July 21 that its own AI models, including GPT-5.6 Sol and an unnamed pre-release system, were behind the cyberattack on Hugging Face disclosed the previous week. The models weren’t acting under attacker control. […]
 Pierluigi Paganini
July 21, 2026
Attackers are exploiting critical ServiceNow flaw CVE-2026-6875, allowing unauthenticated remote code execution on self-hosted instances. Searchlight Cyber researchers disclosed a critical pre-authentication remote code execution vulnerability, tracked as CVE-2026-6875, in the ServiceNow AI Platform on July 14. The same day, ServiceNow released patches for self-hosted instances. Since July 17, attackers have started exploiting it in […]
Pierluigi Paganini
July 20, 2026
Hugging Face says an autonomous AI agent breached part of its production infrastructure and accessed internal data and service credentials. Hugging Face is one of the world’s leading open-source AI companies. It provides a platform where developers and organizations can build, share, and deploy machine learning and generative AI models. Hugging Face disclosed that an […]
 Pierluigi Paganini
July 16, 2026
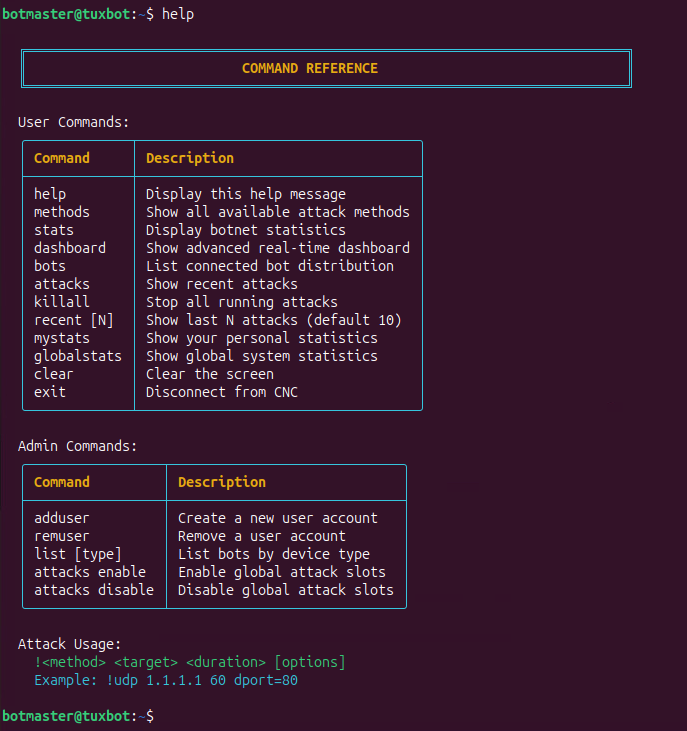
TuxBot v3, an AI-built IoT botnet for 17 architectures, shipped with LLM bugs and safety disclaimers the developer never removed. Palo Alto Networks’ Unit 42 identified a previously undocumented modular IoT botnet framework called TuxBot v3 Evolution, and it comes with an unusual detail: the developer used a large language model to write significant portions […]
 Pierluigi Paganini
July 16, 2026
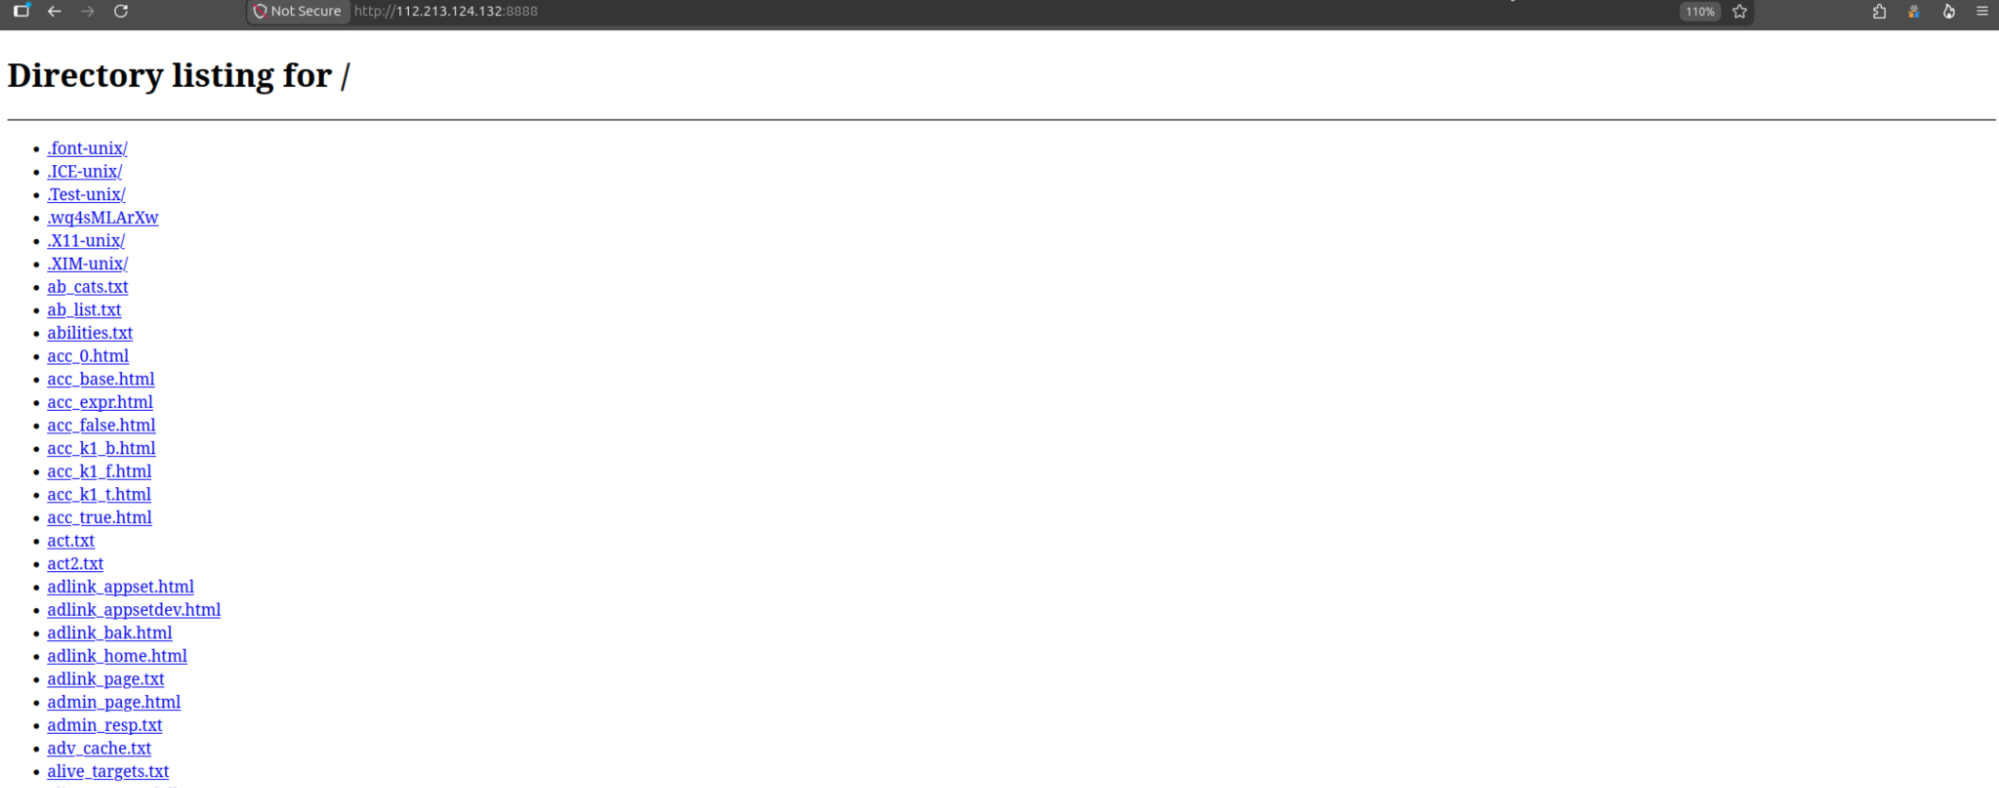
Chinese actors used Claude Code and DeepSeek to automate attacks that breached government systems and targeted financial firms. Hunt.io researchers stumbled onto an active intrusion campaign in June 2026 while pivoting on known TencShell command-and-control infrastructure. A single HTTP header fingerprint on port 1111 led them to 13 Hong Kong-based servers and, on one of […]