 Pierluigi Paganini
 August 02, 2026
After attacks hit 30+ Minnesota water systems, CISA urged utilities to remove internet-exposed PLCs and strengthen OT security. Between Sunday and Monday, July 26 and 27, a coordinated cyberattack hit operational technology (OT) systems at more than 30 community water utilities across the state, according to Minnesota IT Services (MNIT). “A coordinated cyberattack targeted operational technology […]
 Pierluigi Paganini
August 01, 2026
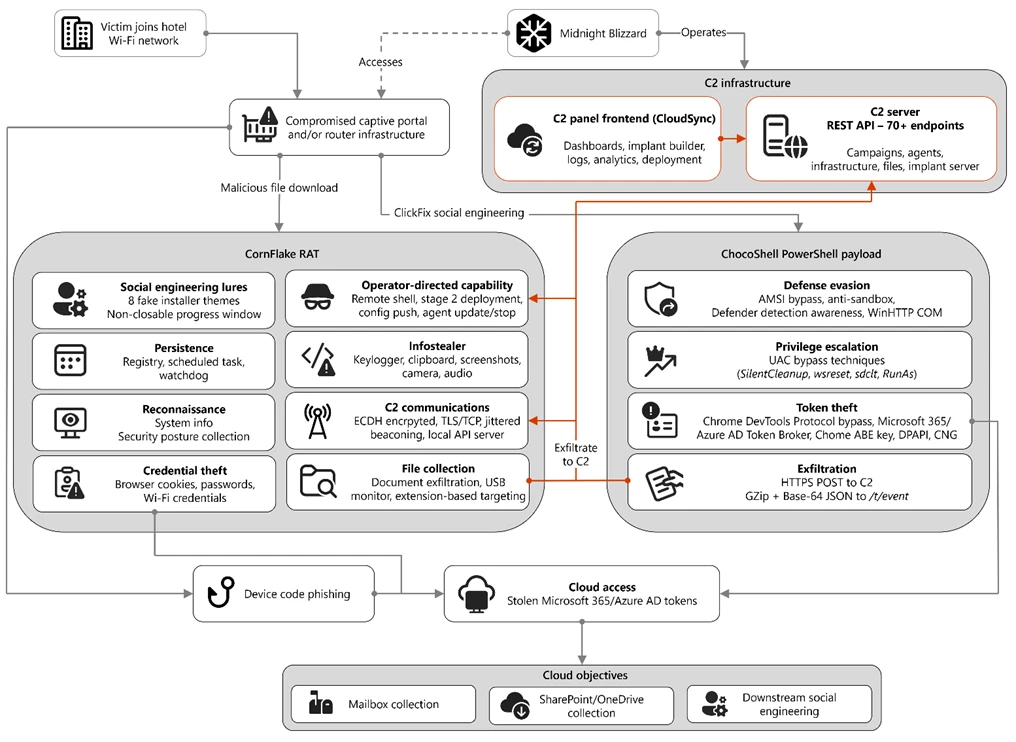
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]
 Pierluigi Paganini
July 31, 2026
South Korea warned that nation-state actors are using phishing and compromised websites to silently infect citizens and businesses. South Korea agencies (The National Intelligence Service, the National Police Agency, the Korea Internet & Security Agency, and the Financial Security Institute) jointly published an advisory warning that a state-backed hacking group is actively targeting South Korean […]
 Pierluigi Paganini
July 31, 2026
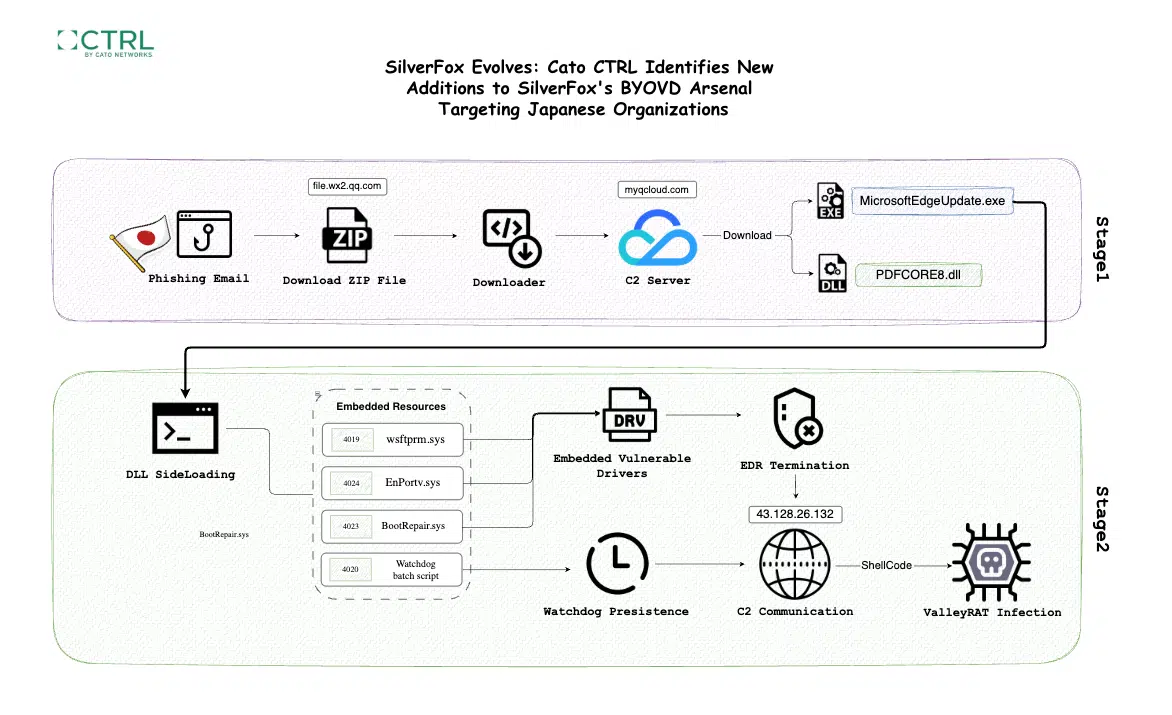
SilverFox targeted a Japanese manufacturer with new DLL sideloading techniques, kernel drivers, and resilient ValleyRAT persistence mechanisms. Cato CTRL documented a new SilverFox campaign targeting a Japanese industrial manufacturer. The attack chain adds two previously undocumented DLL-sideloading hosts, two kernel drivers not previously associated with SilverFox, and a dual-layer recovery architecture that keeps ValleyRAT running […]
 Pierluigi Paganini
July 26, 2026
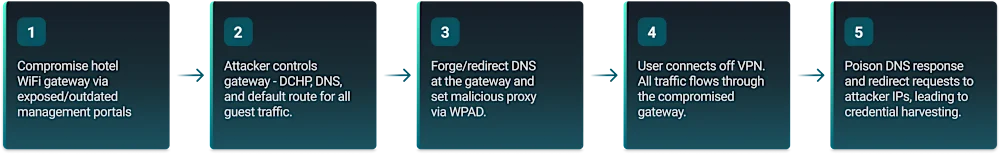
Hackers compromised hotel Wi-Fi gateways to redirect users to fake Microsoft 365 login pages and steal credentials. ReliaQuest’s threat research team just documented attackers compromising the Wi-Fi gateways at hotels and conference centers, then quietly rerouting guests toward fake Microsoft login pages. No phishing email required. No malicious attachment. Just bad luck about which hotel […]
 Pierluigi Paganini
July 25, 2026
US agencies warn Iran-linked actors are targeting internet-exposed water and energy control systems, risking disruption. Federal agencies updated their cybersecurity advisory this week: Iran-linked actors are inside American water and energy control systems, and they’re not just looking around. They’re changing things. The updated advisory from CISA, the FBI, NSA, and the Department of Energy […]
 Pierluigi Paganini
July 24, 2026
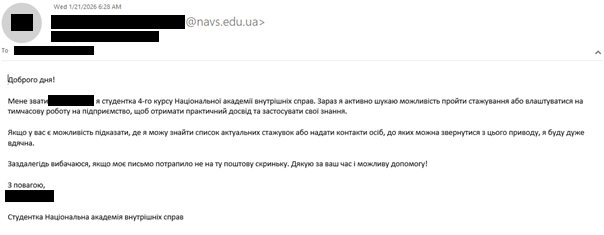
US agencies warn Russian group Laundry Bear is exploiting a patched Zimbra flaw to steal email accounts from organizations running unpatched servers. The Cybersecurity and Infrastructure Security Agency (CISA), National Security Agency (NSA), Federal Bureau of Investigation (FBI) and other U.S. government and international partners published a joint advisory to warn that the Russia-linked APT […]
 Pierluigi Paganini
July 16, 2026
Chinese actors used Claude Code and DeepSeek to automate attacks that breached government systems and targeted financial firms. Hunt.io researchers stumbled onto an active intrusion campaign in June 2026 while pivoting on known TencShell command-and-control infrastructure. A single HTTP header fingerprint on port 1111 led them to 13 Hong Kong-based servers and, on one of […]
 Pierluigi Paganini
July 15, 2026
US and allies warn of Russian APT groups targeting routers and network devices to compromise critical infrastructure worldwide. The US and allied governments warn that Russian state-sponsored APT groups are scanning and exploiting poorly secured network devices, especially routers, to access critical infrastructure. Groups linked to FSB Center 16, including Berserk Bear, Energetic Bear, Ghost […]
 Pierluigi Paganini
July 07, 2026
Armored Likho APT uses AI-generated malware, phishing, and BusySnake Stealer to target governments and power grids in Russia, Kazakhstan, and Brazil. Kaspersky’s threat research team has documented a previously unknown APT group they’re calling Armored Likho, also tracked under the name Eagle Werewolf. The group runs two parallel tracks: financially motivated attacks against private individuals […]