 Pierluigi Paganini
 August 06, 2026
A U.S. court sentenced Ransom Cartel founder Maksim Silnikau to 16 years for running a ransomware-as-a-service operation. Maksim Silnikau (aka “J.P. Morgan,” “lansky,” and “xxx,”) built a ransomware business the way a franchise owner builds a chain: he never had to touch most of the crime scenes himself. This week, a federal judge in Virginia […]
Pierluigi Paganini
August 06, 2026
Snowflake hacker Connor Moucka pleads guilty after breaching 165 organizations, stealing billions of records, and extorting victims. Connor Riley Moucka, 26, of Kitchener, Ontario, pleaded guilty this week to a computer hacking conspiracy that compromised over 165 organizations, stole billions of customer records, and extorted multiple victims for millions of dollars. “Connor Riley Moucka, 26, […]
 Pierluigi Paganini
August 04, 2026
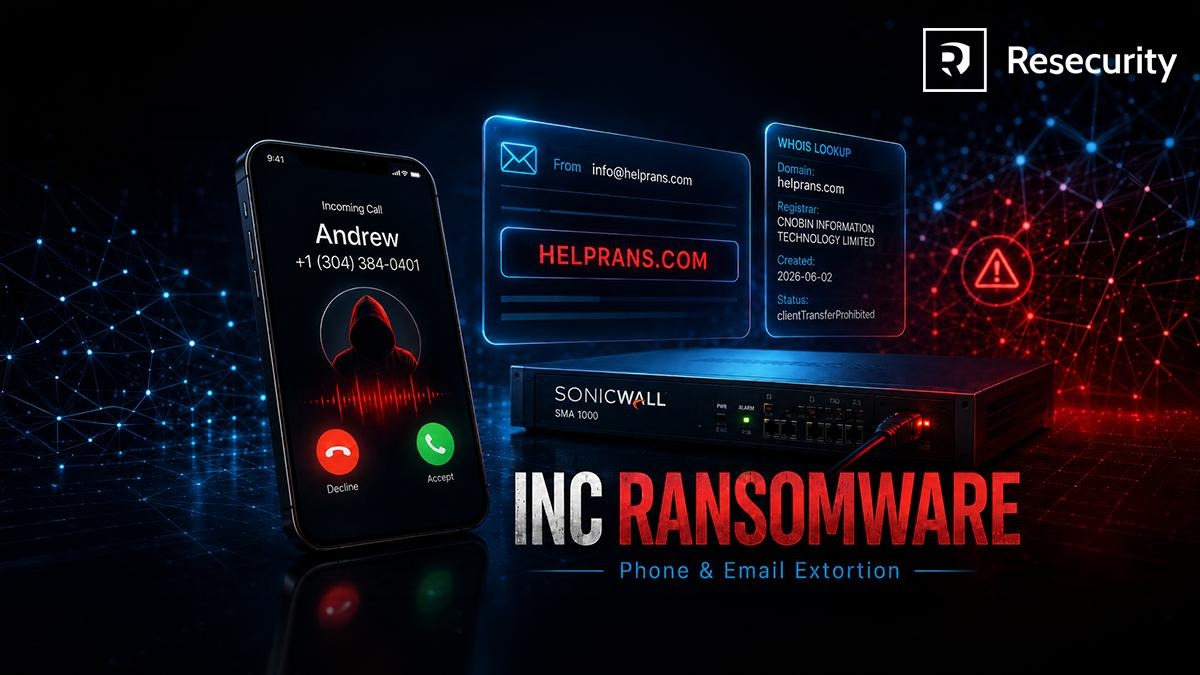
INC Ransomware exploits SonicWall SMA 1000 flaws, using calls and emails to pressure victims during extortion campaigns targeting global organizations. Resecurity disclosed that INC Ransomware has emerged as the dominant threat actor exploiting the recently disclosed SonicWall Secure Mobile Access (SMA) 1000 vulnerabilities. According to the company’s research, the group has accelerated its operations since […]
 Pierluigi Paganini
August 03, 2026
River Bank says hackers deleted data stolen in its June ransomware attack, though the investigation into the incident is still ongoing. River Financial Corporation, the parent company of River Bank & Trust, says hackers deleted data stolen during a ransomware attack that hit parts of its server environment in June. The breach began on June […]
 Pierluigi Paganini
August 02, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter TAG-195 Upgrades MaaS Ecosystem with Modular Tools Inside a DPRK BlueNoroff ClickFix Kit SourTrade: Browser-Assembled Malware Delivered Through Malvertising MedusaHVNC: A Hidden Desktop That Steals Live Windows Sessions Unpacking “Cruciferra”: An Analysis of a […]
 Pierluigi Paganini
August 02, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Russian Hackers Hijack Hotel Wi-Fi to Steal Microsoft 365 Tokens Adobe fixed a maximum-severity vulnerability flaw in […]
 Pierluigi Paganini
August 01, 2026
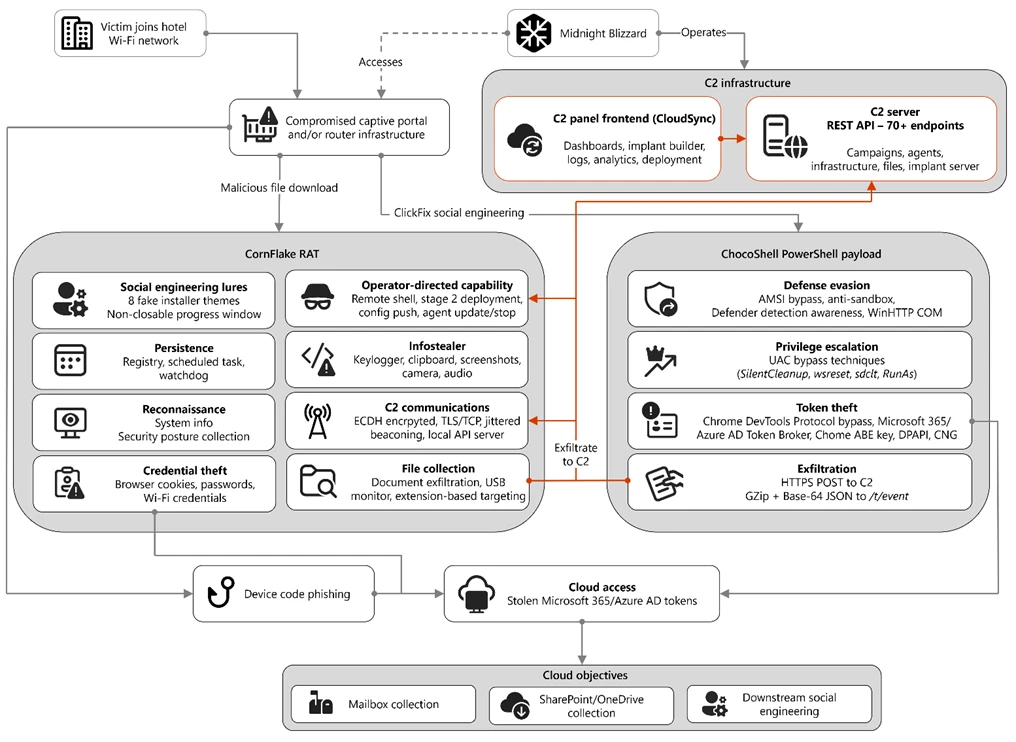
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]
 Pierluigi Paganini
July 31, 2026
South Korea warned that nation-state actors are using phishing and compromised websites to silently infect citizens and businesses. South Korea agencies (The National Intelligence Service, the National Police Agency, the Korea Internet & Security Agency, and the Financial Security Institute) jointly published an advisory warning that a state-backed hacking group is actively targeting South Korean […]
 Pierluigi Paganini
July 31, 2026
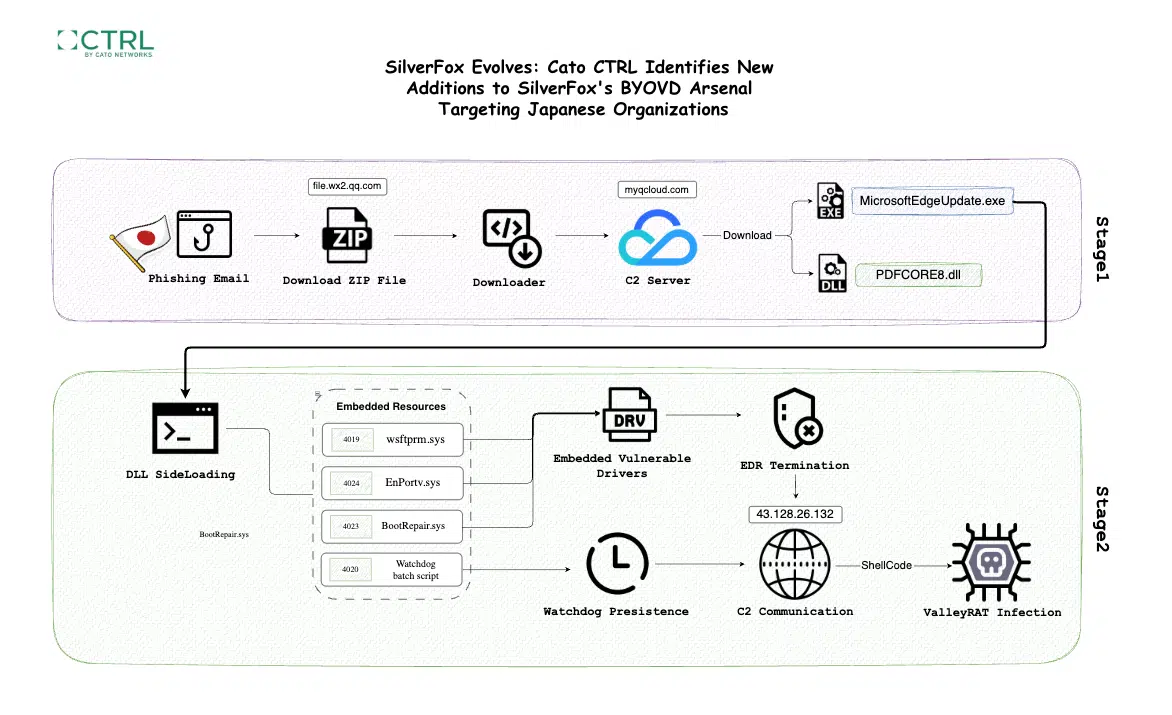
SilverFox targeted a Japanese manufacturer with new DLL sideloading techniques, kernel drivers, and resilient ValleyRAT persistence mechanisms. Cato CTRL documented a new SilverFox campaign targeting a Japanese industrial manufacturer. The attack chain adds two previously undocumented DLL-sideloading hosts, two kernel drivers not previously associated with SilverFox, and a dual-layer recovery architecture that keeps ValleyRAT running […]
 Pierluigi Paganini
July 30, 2026
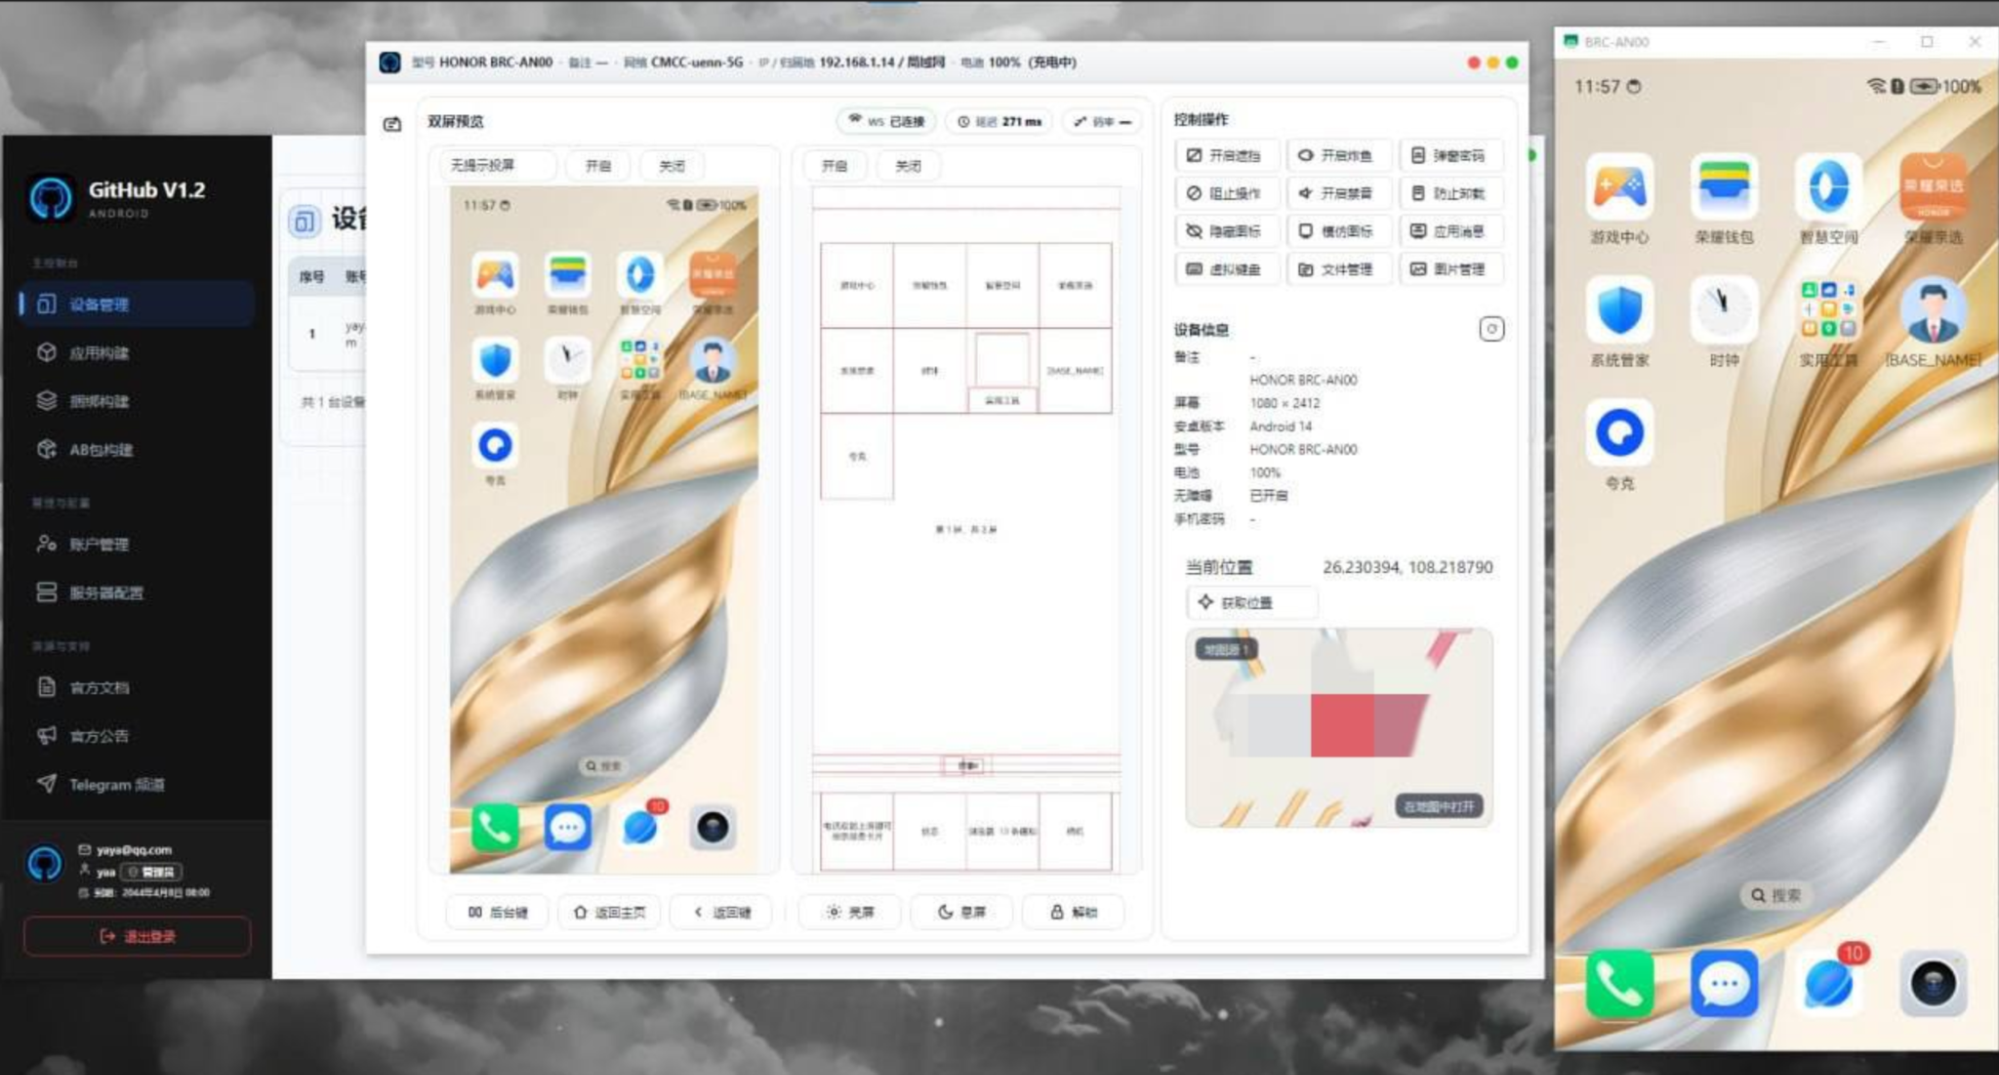
Researchers linked the Flying Eagle Android RAT to fake police apps, uncovering 170 servers in a growing cybercrime ecosystem. Hunt.io researchers and independent journalist NetAskari started with a fraudulent Android app impersonating a Chinese Provincial Public Security Bureau service and ended up mapping a sprawling criminal ecosystem built around a leaked Android RAT framework called […]