 Pierluigi Paganini
 July 17, 2026
Russian-speaking UAT-11795 spreads trojanized Zoom, Webex, and MobaXterm installers to deliver Starland RAT and the WLDR memory-only implant. Cisco Talos researchers published a detailed technical report on July 16 disclosing UAT-11795, a financially motivated, Russian-speaking threat actor that has been running a malware campaign against users in the United States and Europe since at least […]
 Pierluigi Paganini
July 16, 2026
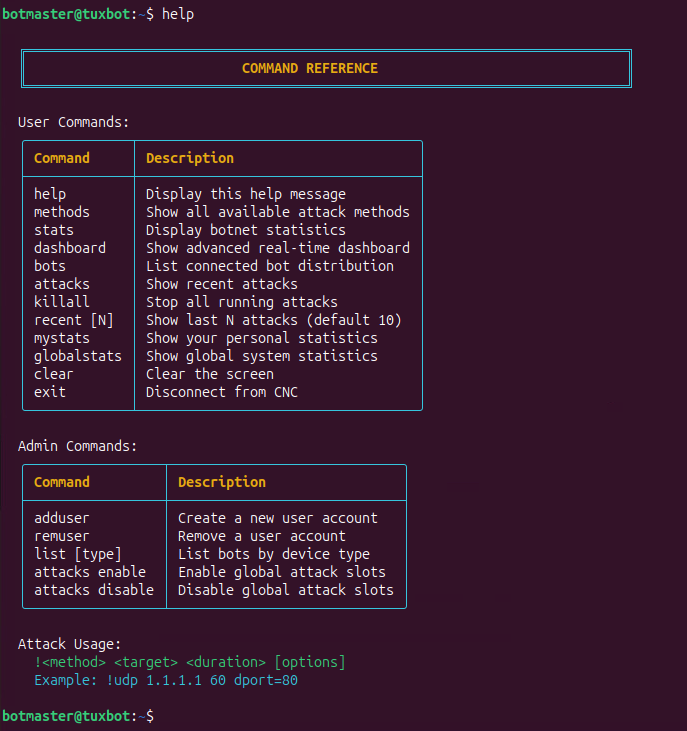
TuxBot v3, an AI-built IoT botnet for 17 architectures, shipped with LLM bugs and safety disclaimers the developer never removed. Palo Alto Networks’ Unit 42 identified a previously undocumented modular IoT botnet framework called TuxBot v3 Evolution, and it comes with an unusual detail: the developer used a large language model to write significant portions […]
 Pierluigi Paganini
July 15, 2026
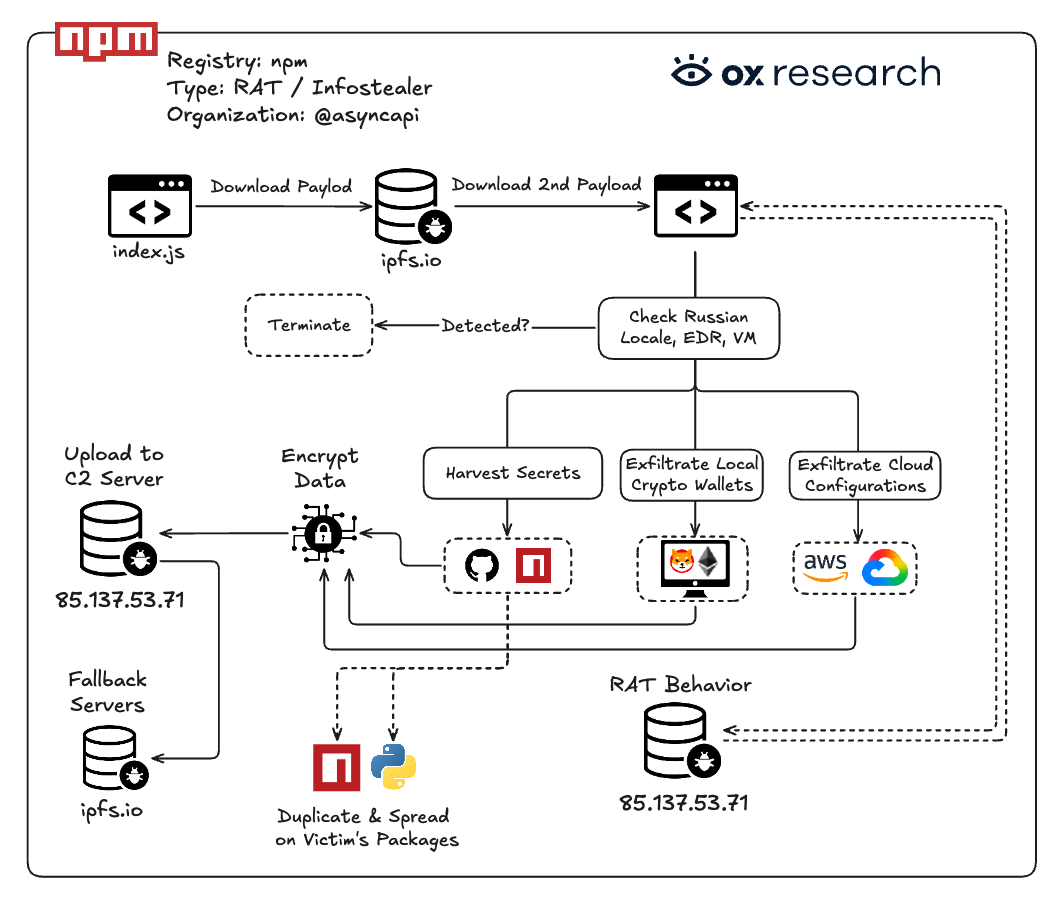
AsyncAPI npm packages with 2M weekly downloads were compromised, spreading malware with info-stealing, crypto-theft and RAT capabilities. OX Security researchers disclosed on July 14 that the AsyncAPI npm organization was compromised, with malicious code injected into four packages that together account for over 2 million weekly downloads. The affected versions are @asyncapi/generator 3.3.1, @asyncapi/generator-components 0.7.1, […]
 Pierluigi Paganini
July 14, 2026
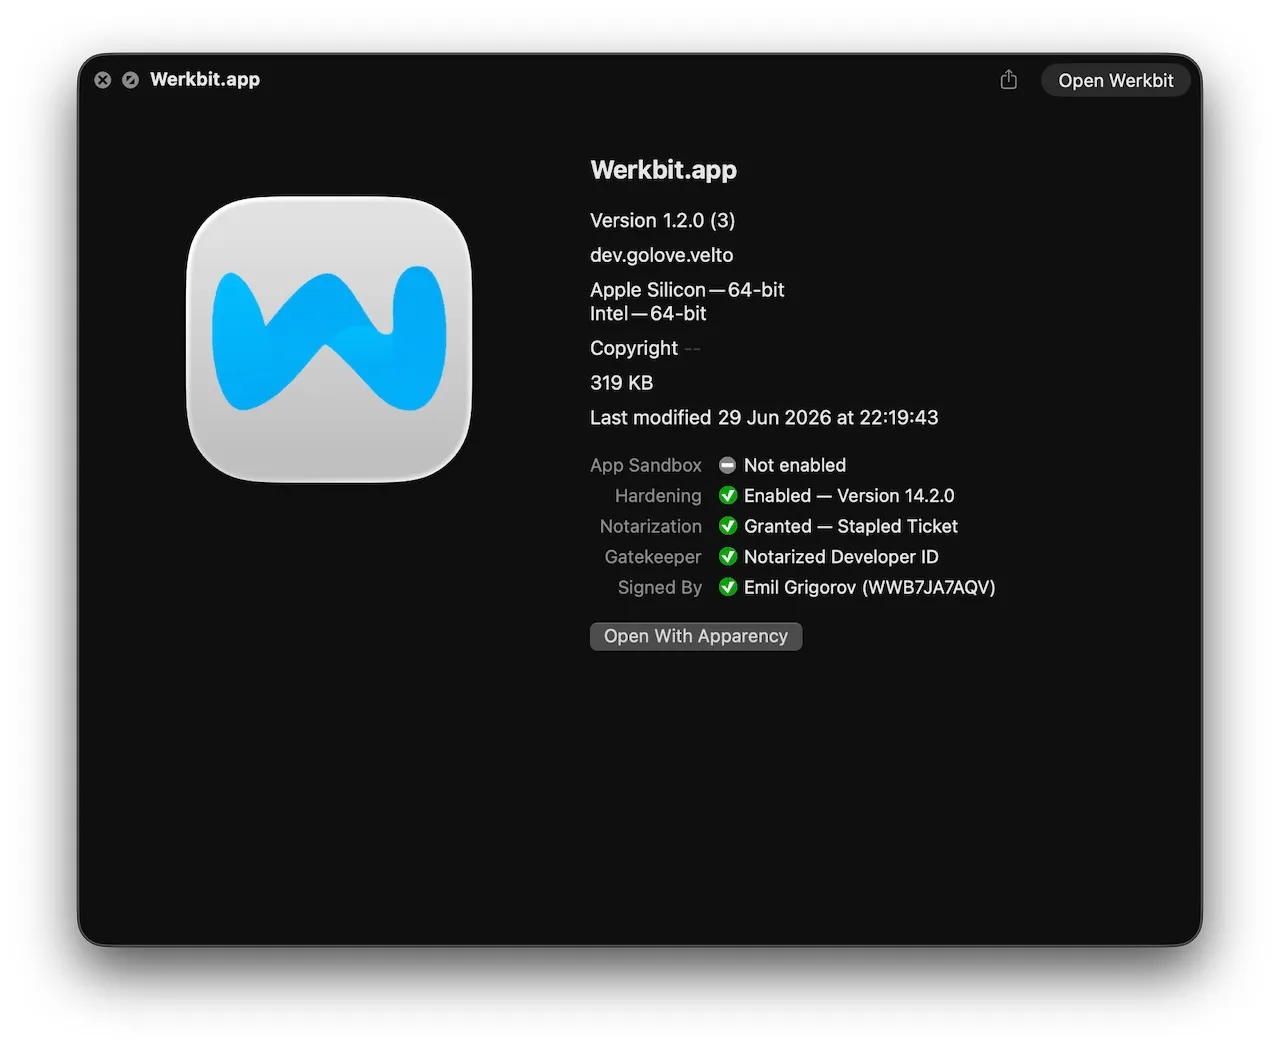
New macOS infostealer CrashStealer uses a signed app to bypass Gatekeeper, steals credentials and wallets, then AES-encrypts stolen data. Jamf Threat Labs first spotted CrashStealer in early May 2026 as a suspicious macOS sample uploaded to VirusTotal. By early July, in-the-wild detections confirmed the malware had moved from development into active deployment. The malware is […]
 Pierluigi Paganini
July 12, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Novel Java-Based QuimaRAT Targets Windows, macOS, and Linux Vibe Coded Extortion: Avalon’s Path from Legal Lure to CrownX Ransom Capabilities Armored Likho digging a snake pit: inside the covert BusySnake Stealer campaign RedWing: A […]
 Pierluigi Paganini
July 10, 2026
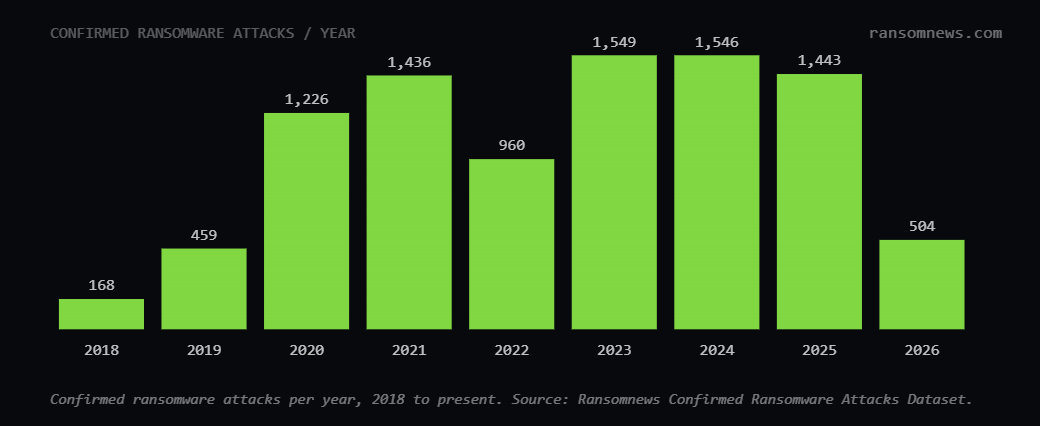
Ransomware remains above 1,400 attacks yearly since 2023. Qilin leads in 2026, while the U.S. remains the main target. Ransomnews has independently confirmed 9,291 ransomware attacks worldwide between January 2018 and July 2026, tracking incidents only when verified through victim disclosures, regulatory filings, official statements, or credible press reporting. Leak-site listings alone don’t qualify, operators […]
 Pierluigi Paganini
July 10, 2026
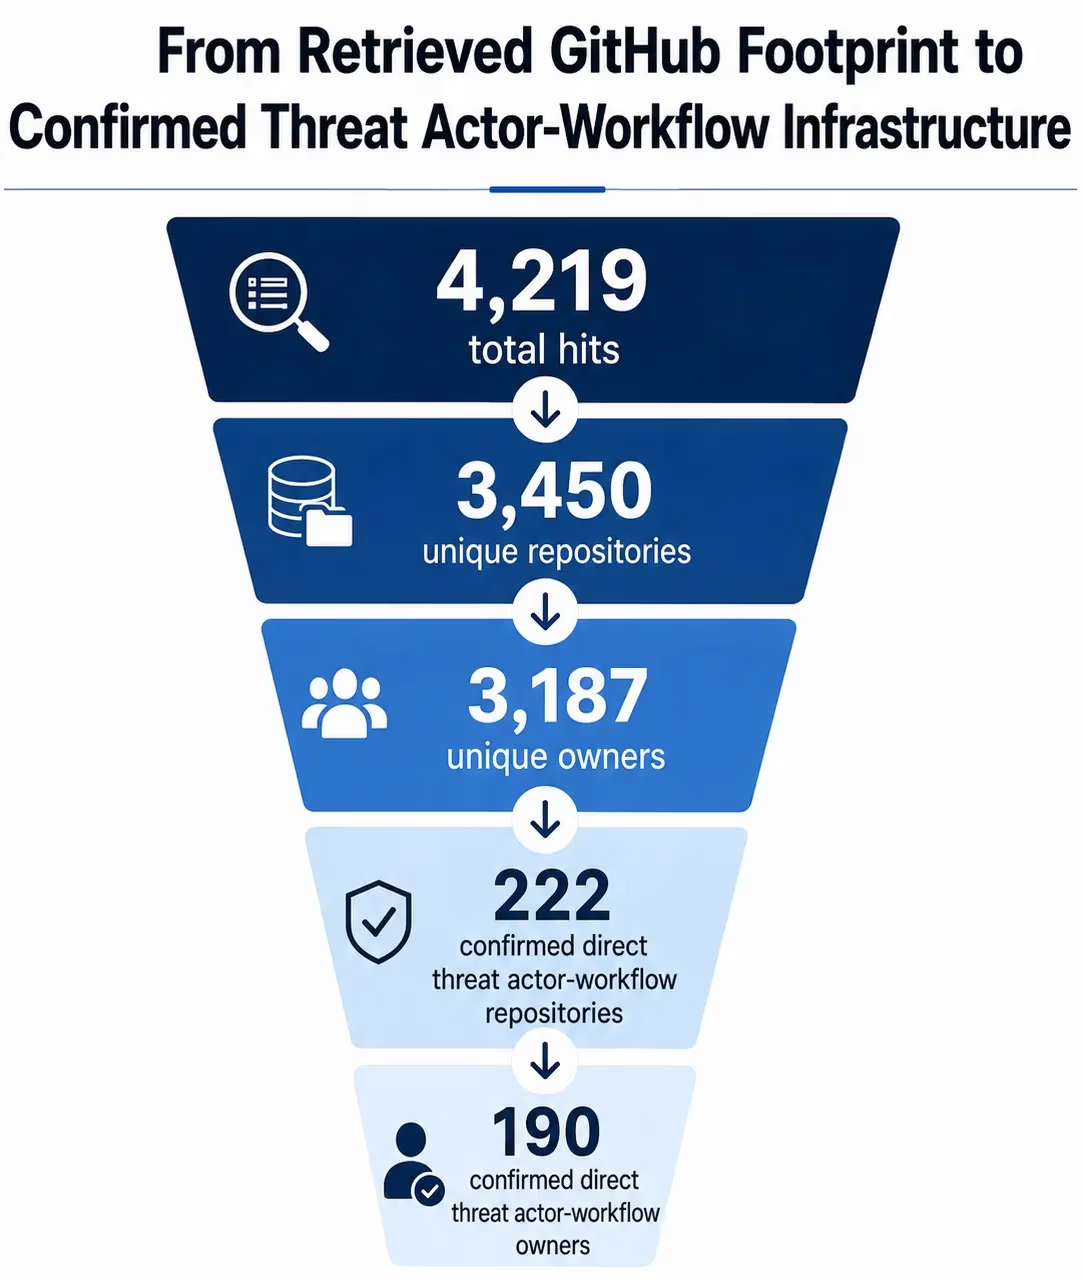
Researchers uncovered 222 GitHub repositories spreading malware through fake Go packages, delivering loaders, stealers, RATs, and cryptominers. Socket’s security research team started with the investigation of a single malicious Go module: github[.]com/kaleidora/dnsub-scanning-tool, which presented itself as a DNS and subdomain scanning utility. Pulling on that thread exposed something significantly larger: a network of 222 confirmed […]
 Pierluigi Paganini
July 10, 2026
A former ransomware negotiator was sentenced to nearly six years for secretly helping BlackCat extort victims while betraying his clients. A U.S. court sentenced former ransomware negotiator Angelo Martino, 41, to 70 months in prison for conspiring with the BlackCat ransomware gang. While negotiating on behalf of five victims, he secretly shared confidential information about […]
 Pierluigi Paganini
July 10, 2026
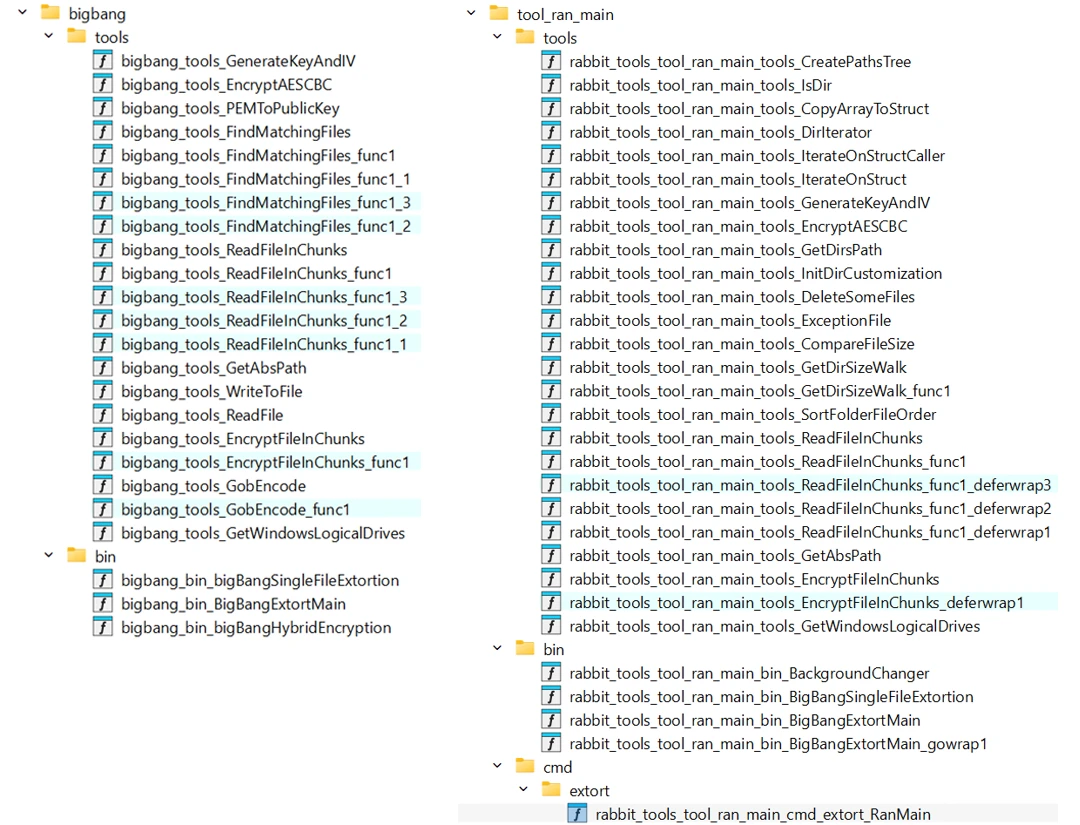
Microsoft uncovered GigaWiper, a modular Go backdoor combining three malware families with espionage, remote control, and destructive wiping features. In October 2025, Microsoft’s threat intelligence team identified destructive wiping activity inside compromised environments and traced it to a previously unknown piece of malware they’re now calling GigaWiper. The malicious code is written in Go, it […]
 Pierluigi Paganini
July 09, 2026
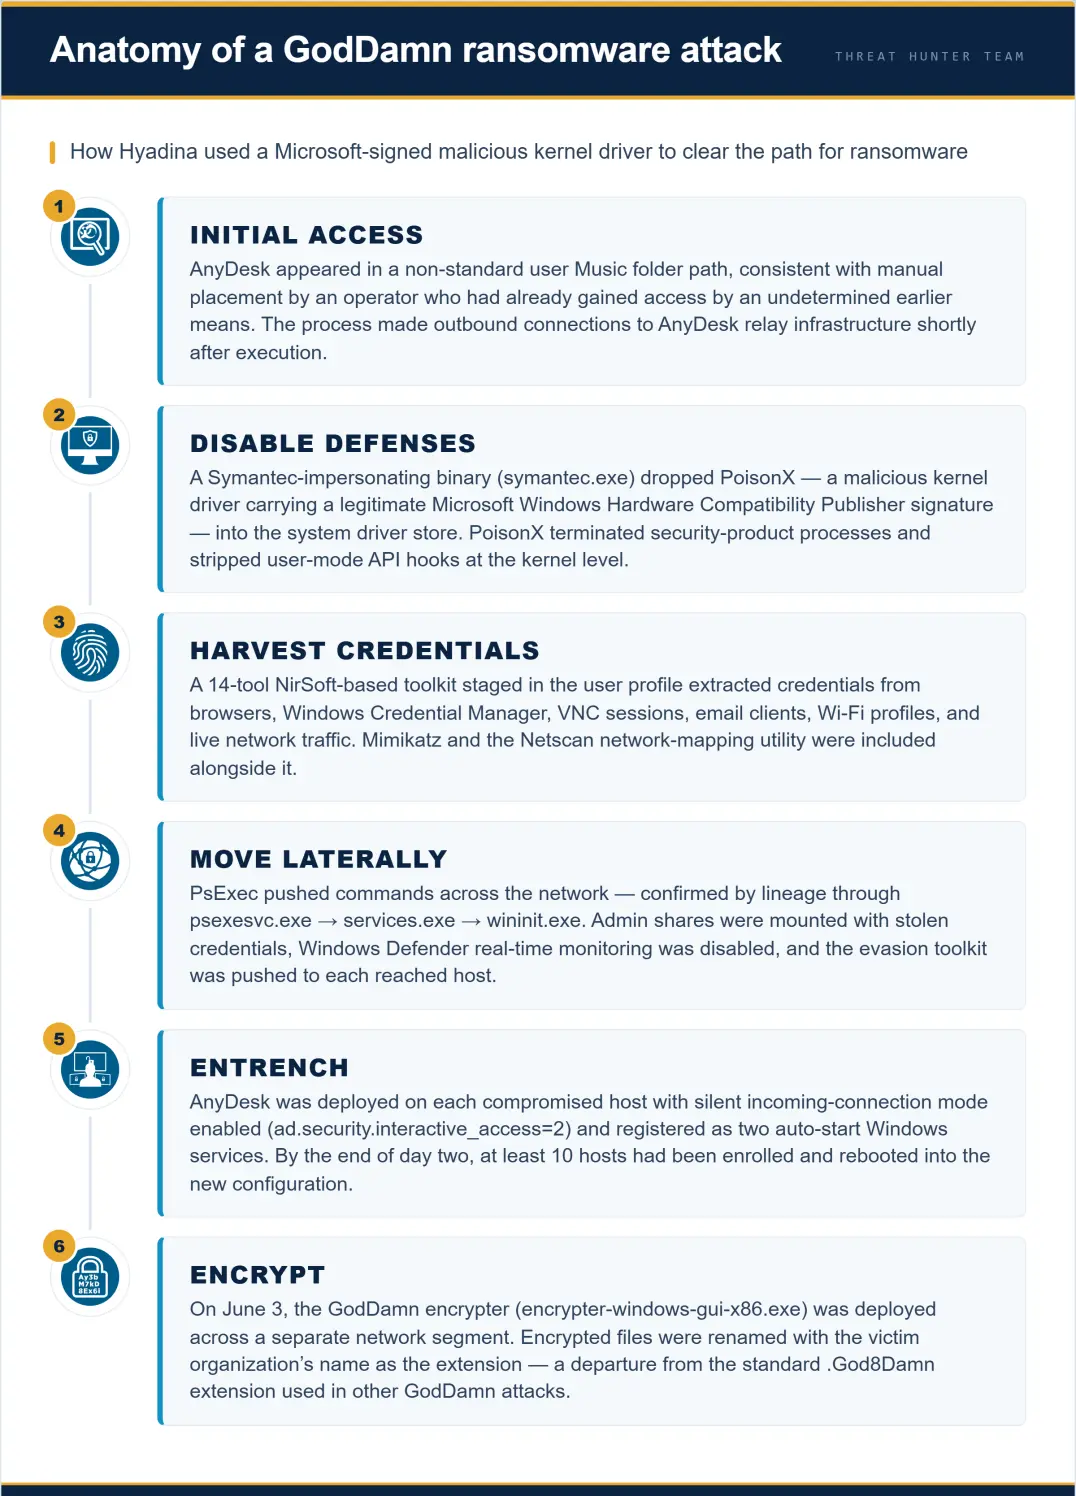
GodDamn ransomware uses the signed PoisonX driver to disable security tools, marking a more advanced version of the Beast ransomware family. Symantec’s Threat Hunter Team found a new ransomware family called GodDamn that first appeared in the wild on May 21, 2026, and analyzed an attack that took place in early June. The group behind […]